
Compliance & Frameworks
ISO 27001, SOC2, NIS2, IT compliance, and compliance automation.
ISO 27001 Certification: The Complete 2026 Guide
Why ISO 27001 Certification Still Matters in 2026. Over 80,000 organizations worldwide now hold ISO/IEC 27001 certification. That number has grown…
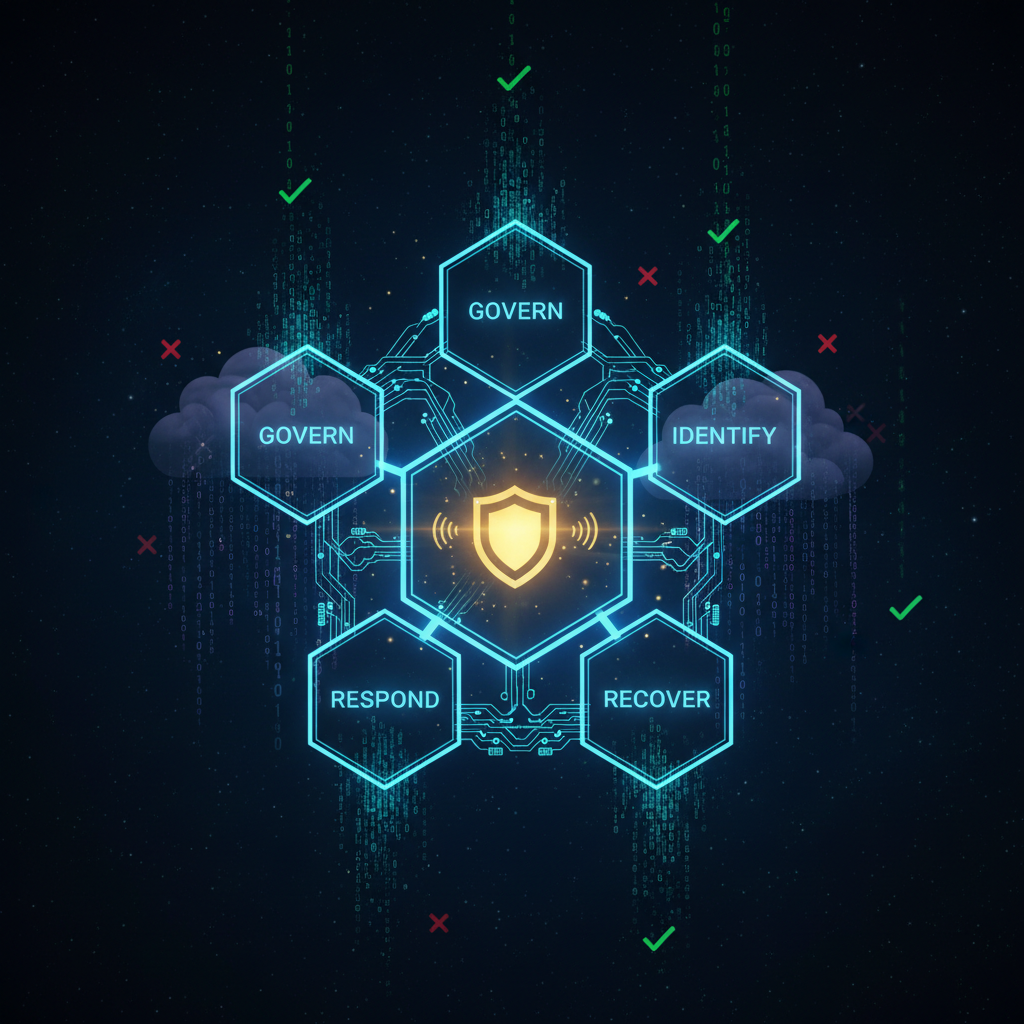
NIST Cybersecurity Framework 2.0: A Practical Guide to Risk Assessment and Compliance
IBM's 2026 Cost of a Data Breach report pegged the average breach cost at $4.88M — and organizations with mature NIST-aligned risk management…
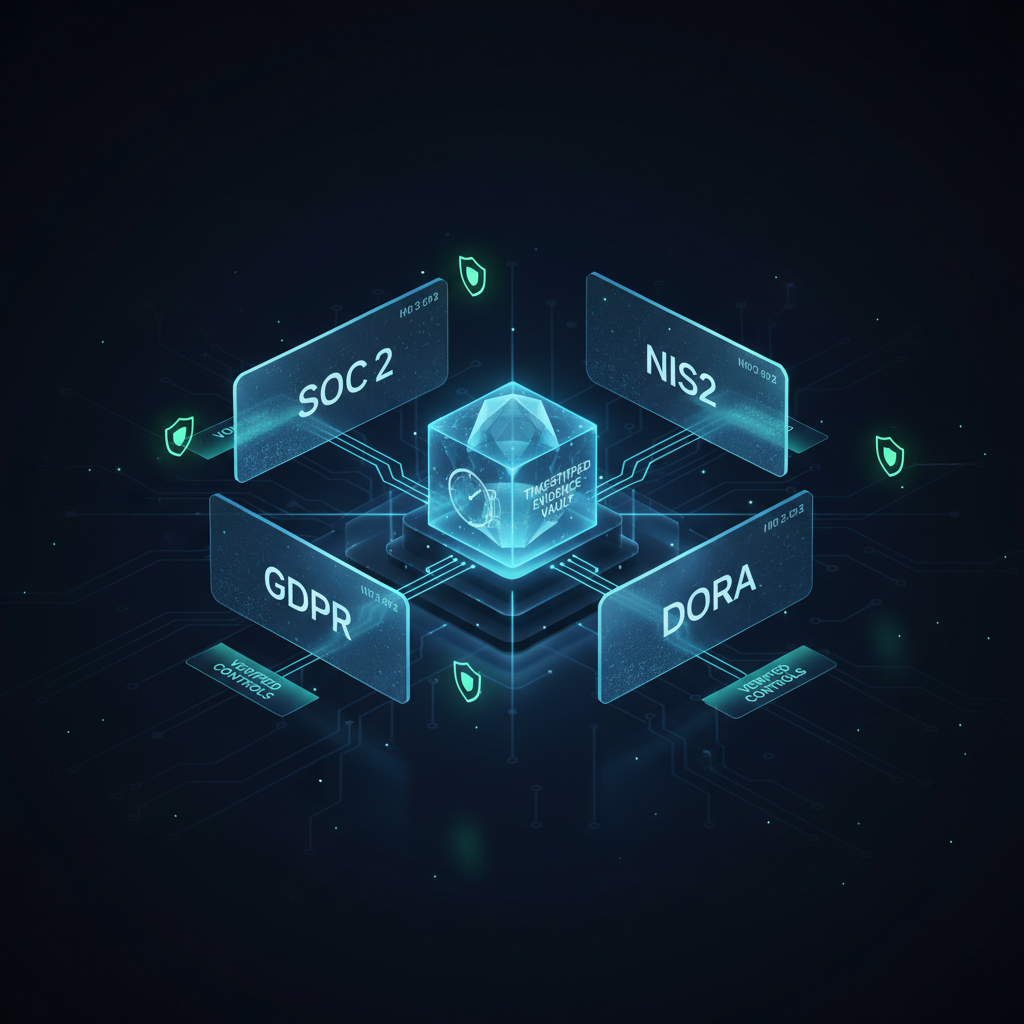
Audit Evidence Collection: A Practical Guide for Modern Compliance Teams
Why Audit Evidence Collection Breaks Most Compliance Programs. Forty-seven percent of organizations that fail a SOC 2 Type II audit cite insufficient…
SOC 2 Compliance: Requirements, Checklist, and Costs Explained (2026)
Roughly 65% of enterprise procurement teams in 2026 require a SOC 2 report before signing a SaaS contract. Not an ISO 27001 certificate, not a…
SOC 2 Compliance: The Complete Technical Guide for 2026
Sixty-three percent of enterprise procurement teams now require a SOC 2 report before signing a SaaS contract. If you are a cloud service provider…
NIS2 Directive: Full Text, Requirements & What It Actually Means for Your Security Team
NIS2 Is Already Law — Are You Actually Ready?. The NIS2 Directive — officially Directive (EU) 2022/2555 — entered into force on January 16, 2023,…
Audit Evidence Collection: The Complete 2026 Guide for SOC 2, NIS2, GDPR, and Beyond
Eighty-three percent of organizations that failed their last compliance audit cited incomplete or poorly organized evidence as the primary reason.…
Compliance Management Systems: A Practical Guide for 2026
Roughly 60% of organizations facing a regulatory action in 2026 had a compliance program in place — it just was not automated. That is the…
DORA Regulation: Complete Guide to the Digital Operational Resilience Act in 2026
January 17, 2025 was the deadline. After a two-year implementation window, the Digital Operational Resilience Act — DORA — became fully applicable…